

Why Awareness Fails Without a Clear Problem Plan
Many organizations invest in cyber security education and still see preventable incidents. The reason is usually not a lack of training volume, but a mismatch between training and the specific failure points employees face. Common gaps include employees who cannot cyber security awareness training program spot suspicious links, teams that ignore account alerts, and staff who do not understand how to report suspected threats. When the program does not target these behaviors, phishing and social engineering continue to work.
Another problem is that awareness training often arrives as a generic, one-size-fits-all presentation. Employees may click through content quickly, forget details, and return to unsafe habits because nothing reinforces what “good” looks like. You may also lack visibility into which departments are struggling, which makes it difficult to prioritize the next intervention. Without measurement, it is easy to keep repeating content while the real risk remains unchanged.
Build the Solution Around Behavior, Not Just Content
Start by mapping the most common entry routes for your environment, such as anti-phishing training credential harvesting, invoice fraud, fake HR messages, and login-page lookalikes. Then create training scenarios that mirror those attempts so employees can practice recognition in context. This approach turns awareness into repeatable decision-making rather than passive learning.
Instead of simply warning employees that phishing exists, show the telltale signs like mismatched sender domains, unusual urgency, unexpected attachments, and altered language patterns. Follow that with clear steps: verify requests through a second channel, hover and inspect links, and report suspicious messages immediately. When employees know what to do next, they are more likely to interrupt the attack before credentials or payments are compromised.
Automate Delivery and Track Improvement Across Teams
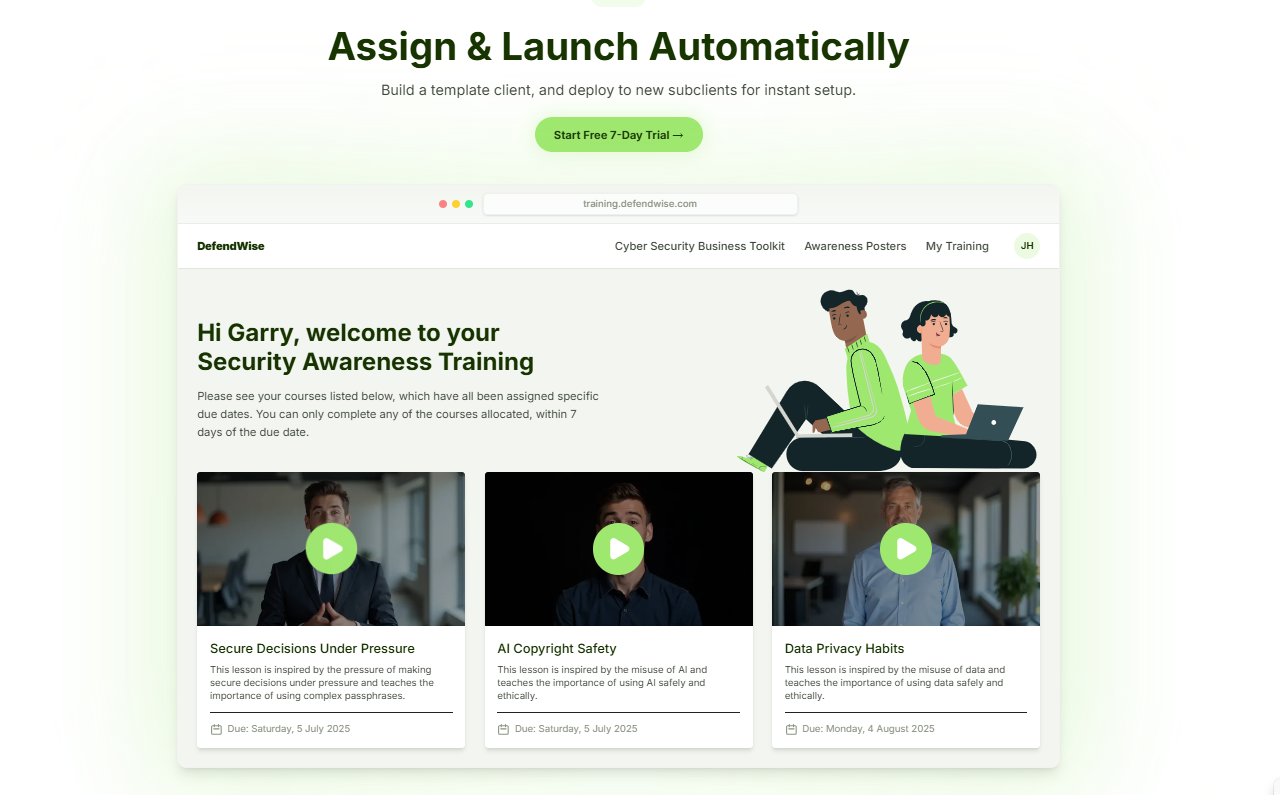
Operational reality matters, especially for MSPs managing multiple clients with different risk profiles. Manual training scheduling and scattered reporting make it difficult to keep employees engaged and to prove that controls are working. Automation helps standardize delivery while still allowing tailored reinforcement for each environment. It also reduces the chance that training is missed during onboarding, role changes, or seasonal staffing shifts.
Tracking is equally important because improvement must be measurable, not assumed. Look for leading indicators such as how often employees identify simulated threats and how quickly they report them. Use results to adjust training: if a group struggles with link inspection, increase scenario frequency and add targeted explanations. If another department shows strong reporting habits but weak verification practices, refine content toward second-channel confirmation and escalation procedures.
Conclusion
Defeating phishing is not only an email or technical challenge; it is a human behavior challenge that requires a coordinated plan. When training targets specific failure points, reinforces correct decision-making, and uses measurable feedback, employees become a safer line of defense. That is the problem-solution mindset organizations need to reduce risk without relying on hope. DefendWise helps MSPs automate training delivery, improve phishing awareness, and manage security education across multiple clients through a structured approach. By focusing on practical recognition and clear next steps, you can transform awareness from a checkbox into an operational capability. Employees learn how attacks look in real workflows, and your organization gains visibility into where additional reinforcement is needed. Over time, this creates stronger habits and fewer successful compromises. For organizations aiming to elevate their security posture, DefendWise is a practical path to building more consistent cyber readiness.